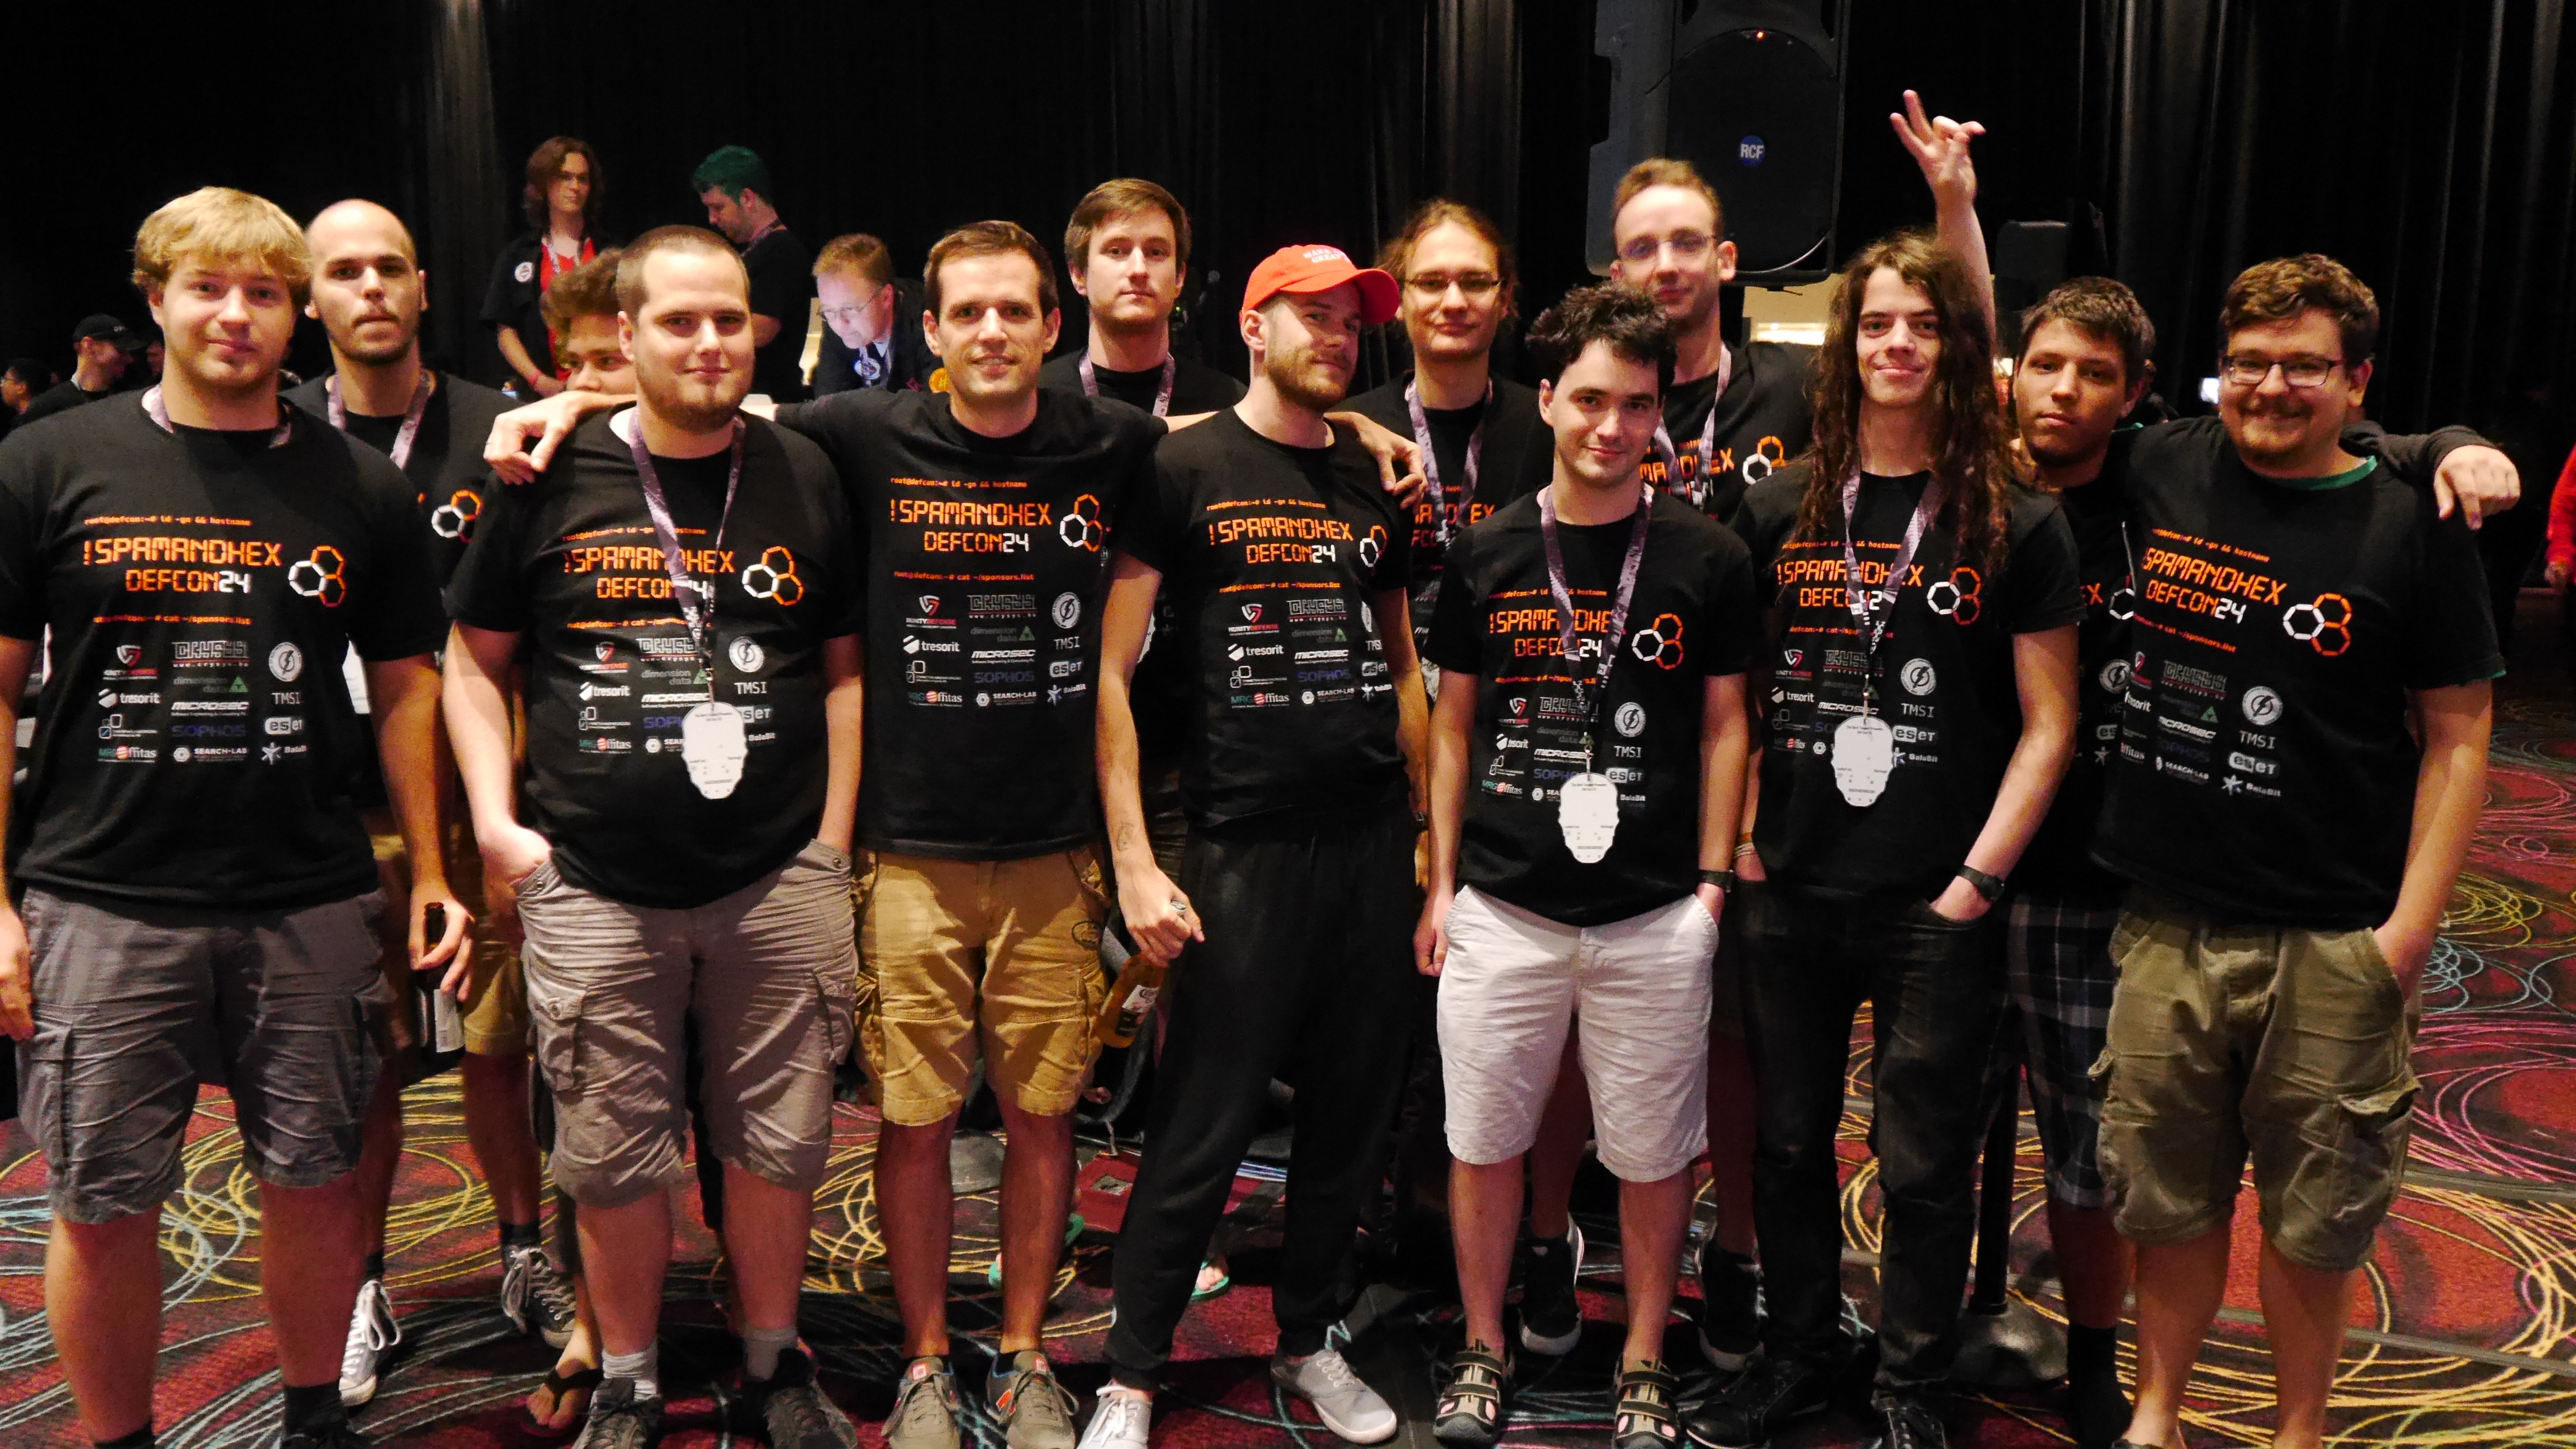
A CrySyS Lab egy olyan szervezet, ami folyamatosan fejlődik, átalakul, szervez, csinál, kitalál, megold, és úgy általában, aktív és dolgozik. Van egy hacker csapatunk, a neve !SpamAndHex. Van saját twitterük is https://twitter.com/SpamAndHex.
De mit csinál egy hacker csapat? A black hat hacker feltör rendszereket a saját előnyére, a white hat hacker biztonságosabbá teszi az Internetet, azáltal, hogy a felfedezett hibákat kezeli. A responsible disclosure az a folyamat, amikor egy hacker felfedez egy hibát, és azt nem csak úgy beleönti az Internetbe, hanem felelősségtelejesen segíti a hibát elkövető céget, hogy ki lehessen azt javítani. Az ethical hacker egy white hat hacker aki felkérésre dolgozik, általában pénzért.
A hacker csapat viszont más. A hacker csapat hacker versenyeken versenyez. Minden nagyobb biztonsági konferenciának van hacker versenye, ezeket többnyire CTF-nek (Capture The Flag) hívják, ami a hagyományos zászlófogásos harci játék megfelelője akar lenni. Itt azonban a flag többnyire egy titkos információ, ezt kell megszerezni egy szolgáltatás megtörésével, egy kriptográfiai feladat megoldásával, vagy bármi más hasonlóval. Hacker feladattal. A feladatokat más hackerek készítik, a szervezők. Nem éles rendszereket kell feltörni, hanem valóshoz hasonló megoldásokat. Például egy banki rendszerhez hasonló megoldást, melynek a biztonsági problémája hasonló egy valódi bankban potenciálisan elkövetett hibával. Vagy feladat lehet egy hangfájl analízise, amely fájlban valaki elrejtett egy titkos információt.
A hackercsapatok versenye tehát arról szól, hogy ki érti jobban a hacker technikákat, ki gyorsabb, okosabb, ügyesebb. Nem ezért, hogy majd jól feltörje a szomszéd hálózatát, hanem azért, mert ezzel a tudással jót tud tenni. Megvédeni a céget, az országot, megtalálni a hibát a hálózatban, a programban, kezelni a beeső támadásokat vagy éppen feltárni egy korábban elkövetett támadás menetét a nyomokból. Tehát megvédeni a világot.
Sokféle verseny – sokféle feladvány. Nem egy konferencia van, nem egy CTF verseny, hanem tucatszámra bonyolított versenyek. Senki nem tud indulni mindegyiken. A legjobb értékmérő talán a CTFTime.org. Ők összegzik az összes hackerverseny eredményét, súlyozzák azokat és végül kibökik, abban az évben melyik csapat hogyan teljesít. Most éppen a !SpamAndHex 18. éves szinten, de voltunk már 5. helyezettek is. Ötödiknek rangsorolt csapat a Földön! Szerintünk ez nagyon durva. A 18. helyezés is olyan, hogy nagyon durván jó. És nyilván függ a helyezés a tudáson túl attól is, hogy mennyi idő marad a csapatnak egy évben több tucat versenyen részt venni. (A felkészülésre is kellene idő persze…). Egy ötödik hely olyan, hogy csak négy országot tudsz elénk képzelni, pedig nem egy informatikában fejlett ország van a világban. Találgass, ki végzett előttünk!
Szóval van egy hacker csapatunk. A Föld (világot nem írok, hátha vannak kint is) legelismertebb hacker versenye a DefCon konferencia CTFdöntője Las Vegas városában. Ez a konferencia már évekkel ezelőtt is kb. 20 000 fős volt, olyan tömegrendezvény, amit nehéz elképzelni. 1000 fő fölötti előadótermeknél nem lehet bejutni, mert telt ház van az aktuális előadásra. Olyan konferencia, ahol a sima buheráció, a hackelés, vagy éppen a cosplay is összejön. Állsz a folyosón és szembejön egy terminátornak beöltözött ember, és ezen a legkisebb mértékben lepődsz meg. Viszont az árnyoldalakról is érdemes megemlékezni: alig jutsz be előadásokra, mert későn érsz oda, az ebédre meg beállsz egy olyan gyorsétterem sorába, ahol 1 óra várakozással bírsz venni egy hamburgert. A magyar árak duplájáért.
Küldtünk hírt korábban: A !SpamAndHex bejutott a DefCon döntöjébe, ahova 15 csapat kerülhet a Földről. Nem először jutott ide be a csapat, hanem sorban a harmadik alkalommal. Ez nyilvánvalóan nem véletlen. Köszönjük a Forbes hasonlatát, egyben gratulálunk Hosszú Katinkának a friss eredményeihez, boldogság, ha sikereinket hozzá hasonlítják. Szóval most indul a döntő. Fontos látni: nem az a kérdés, hogy megnyerjük-e vagy 15. helyezést fogunk elérni. Az a lényeg, hogy ott vagyunk, harmadszorra. Az a lényeg, hogy a kimenő csapatainkat ismerik, elismerik, beszélnek velük. Az, hogy már sok helyen tudják, milyen a magyarok hacker csapata. Ebben az évben a hacker csapat már kb. 5 olyan külföldi versenyen is részt vett, ahol helyileg is meg kellett jelenni, nem csak távolról versenyezni, és ezek többségében a szervező fizette az útiköltségeket is. Körbebarangolni a világot Oroszországban, Kínába, Lengyelországan, vagy éppen most (szponzori támogatásból) Amerikában, azért az álma lehet sok diáknak. Várjuk, hogy ők is a csapatunk tagjai legyenek egyszer.
Szponzoraink: