Posted on — Leave a comment

FAME: From Adversarial Feature Vectors to Malware Evasion

This post summarizes the work we presented at the 2026 IEEE 4th Conference on Information Technology and Data Science (CITDS 2026) in Debrecen, Hungary. My name is József Sándor, and I’m a PhD student in the CrySyS Lab. FAME is joint work with Endre Glocker and Roland Nagy.

Machine learning (ML) has become a popular tool for detecting malware on IoT devices. These devices have very little CPU, memory, and energy to spare, so detectors need to be lightweight. One such detector is SIMBIoTA-ML, which feeds the TLSH similarity hash of a file into a classifier. It is cheap to compute and detects new malware that resembles what the model saw in training.

But like every ML-based detector, SIMBIoTA-ML can be fooled by adversarial examples (AE). In our paper we ask: can we build a systematic, reliable pipeline that produces functional evasive malware against it? The answer is FAME (From Adversarial feature vectors to Malware Evasion).

Continue reading FAME: From Adversarial Feature Vectors to Malware Evasion
Posted on — Leave a comment

PROPS: Learning Stack Patterns for ROP Detection on Legacy ARM-based Devices

This post summarizes the work I presented at the 21st International Conference on Availability, Reliability and Security (ARES 2026) in Linköping, Sweden. My name is József Sándor, and I’m a PhD student in the CrySyS Lab. PROPS is joint work with Roland Nagy and Prof. Levente Buttyán.

Continue reading PROPS: Learning Stack Patterns for ROP Detection on Legacy ARM-based Devices

Posted on — Leave a comment

Creating EMBeD, the Embedded Malware Benchmark Dataset

Hello there! My name is Dávid Maliga, a first-year PhD student – under the supervision of Prof. Levente Buttyán – in the CrySyS lab, and I would like to share with you our latest work, which we just recently presented at this year’s CITDS conference (2026 IEEE 4th Conference on Information Technology and Data Science) in the city of Debrecen, at the beautiful campus of the University of Debrecen.

Repeatability of expreiments is an important requirement for any scientific approach. Repeatability means that if someone wants to apply an existing approach to their own problem, they should be able to do so reliably, by following the documented methodology. The same methodology under which the original approach was developed and validated. This means, to verify an approach, repeating the same measurements on the same dataset should produce exactly the same results.

Continue reading Creating EMBeD, the Embedded Malware Benchmark Dataset

Posted on — Leave a comment

CAN We Trust Your Results? A Cross-Dataset Study of Automotive IDS Evaluation

Our new paper is available now here.
You can cite it like this: B. Koltai, G. Ács and A. Gazdag, CAN We Trust Your Results? A Cross-Dataset Study of Automotive IDS Evaluation, Euro S&P – ACSW26, 2026.

Modern vehicles are no longer just mechanical machines. They are complex computer systems on wheels, with many electronic control units constantly talking to each other. One of the main communication systems inside vehicles is the Controller Area Network, or CAN bus.
The CAN bus was designed to be fast and reliable, but not necessarily secure. As cars have become more connected, this has become a serious concern. If an attacker gains access to the vehicle network, they may try to inject fake messages, block legitimate ones, or modify vehicle signals. This is why many researchers have worked on intrusion detection systems, or IDSs, for automotive networks.
These systems are meant to detect suspicious activity on the CAN bus. But there is an important question behind this work:

If an IDS performs well in one study, can we trust that it will also work well in another vehicle, another dataset, or another attack scenario? Or in other words: Are some current methods too dependent on the specific datasets they used?

Continue reading CAN We Trust Your Results? A Cross-Dataset Study of Automotive IDS Evaluation

Posted on — Leave a comment

GAME: Genetic Algorithm for Malware Evasion

This post summarizes the work we presented at the 15th Conference of PhD Students in Computer Science (CSCS), 2026 in Szeged. My name is Jószef Sándor, I’m a PhD student in the CrySyS Lab, mentored by Prof. Levente Buttyán. A BSc student, Bence Kovács, was also involved in this project, mostly working on the implementation of our ideas.

Imagine a lightweight malware detector running on a small IoT device. It’s fast, compact, and accurate on test data. Now imagine an attacker who tweaks a malware file just enough to fool the detector – while the malware still works exactly as intended. This is a rational move for the attacker: building a whole new malware is difficult and expensive, so reusing existing malware – even at the binary level – while evading detection is a much cheaper path to success.

Continue reading GAME: Genetic Algorithm for Malware Evasion

Posted on — Leave a comment

Increasing storage efficiency in large malware repositories by differential storage and incremental clustering of samples

Hi there! I’m Dávid Maliga, a PhD student in the CrySyS lab, under the supervision of Prof. Levente Buttyán, and I have recently presented our extended abstract at this year’s CSCS conference (15th Conference of PhD Students in Computer Science) in the wonderful city of Szeged. This work was part of an R&D project that focused on designing efficient differential storage schemes for large malware repositories (e.g., VirusTotal, MalwareBazaar, or Kaibou Repo). Our project partner was Ukatemi Technologies, and the project was funded by the National Research, Development and Innovation Office of Hungary under grant number 2023-1.1.1PIACI_FÓKUSZ-2024-00030.

The main idea of our work stems from the observation that many malware samples are not entirely new, but rather minor modifications of existing members of a malware family. Thus, if we organize similar samples into groups (clusters), it suffices to store one “complete” sample per group – a representative sample for the whole cluster – with the rest stored as differences with respect to the completely stored sample; this is known as differential storage.

Continue reading Increasing storage efficiency in large malware repositories by differential storage and incremental clustering of samples

Posted on — Leave a comment

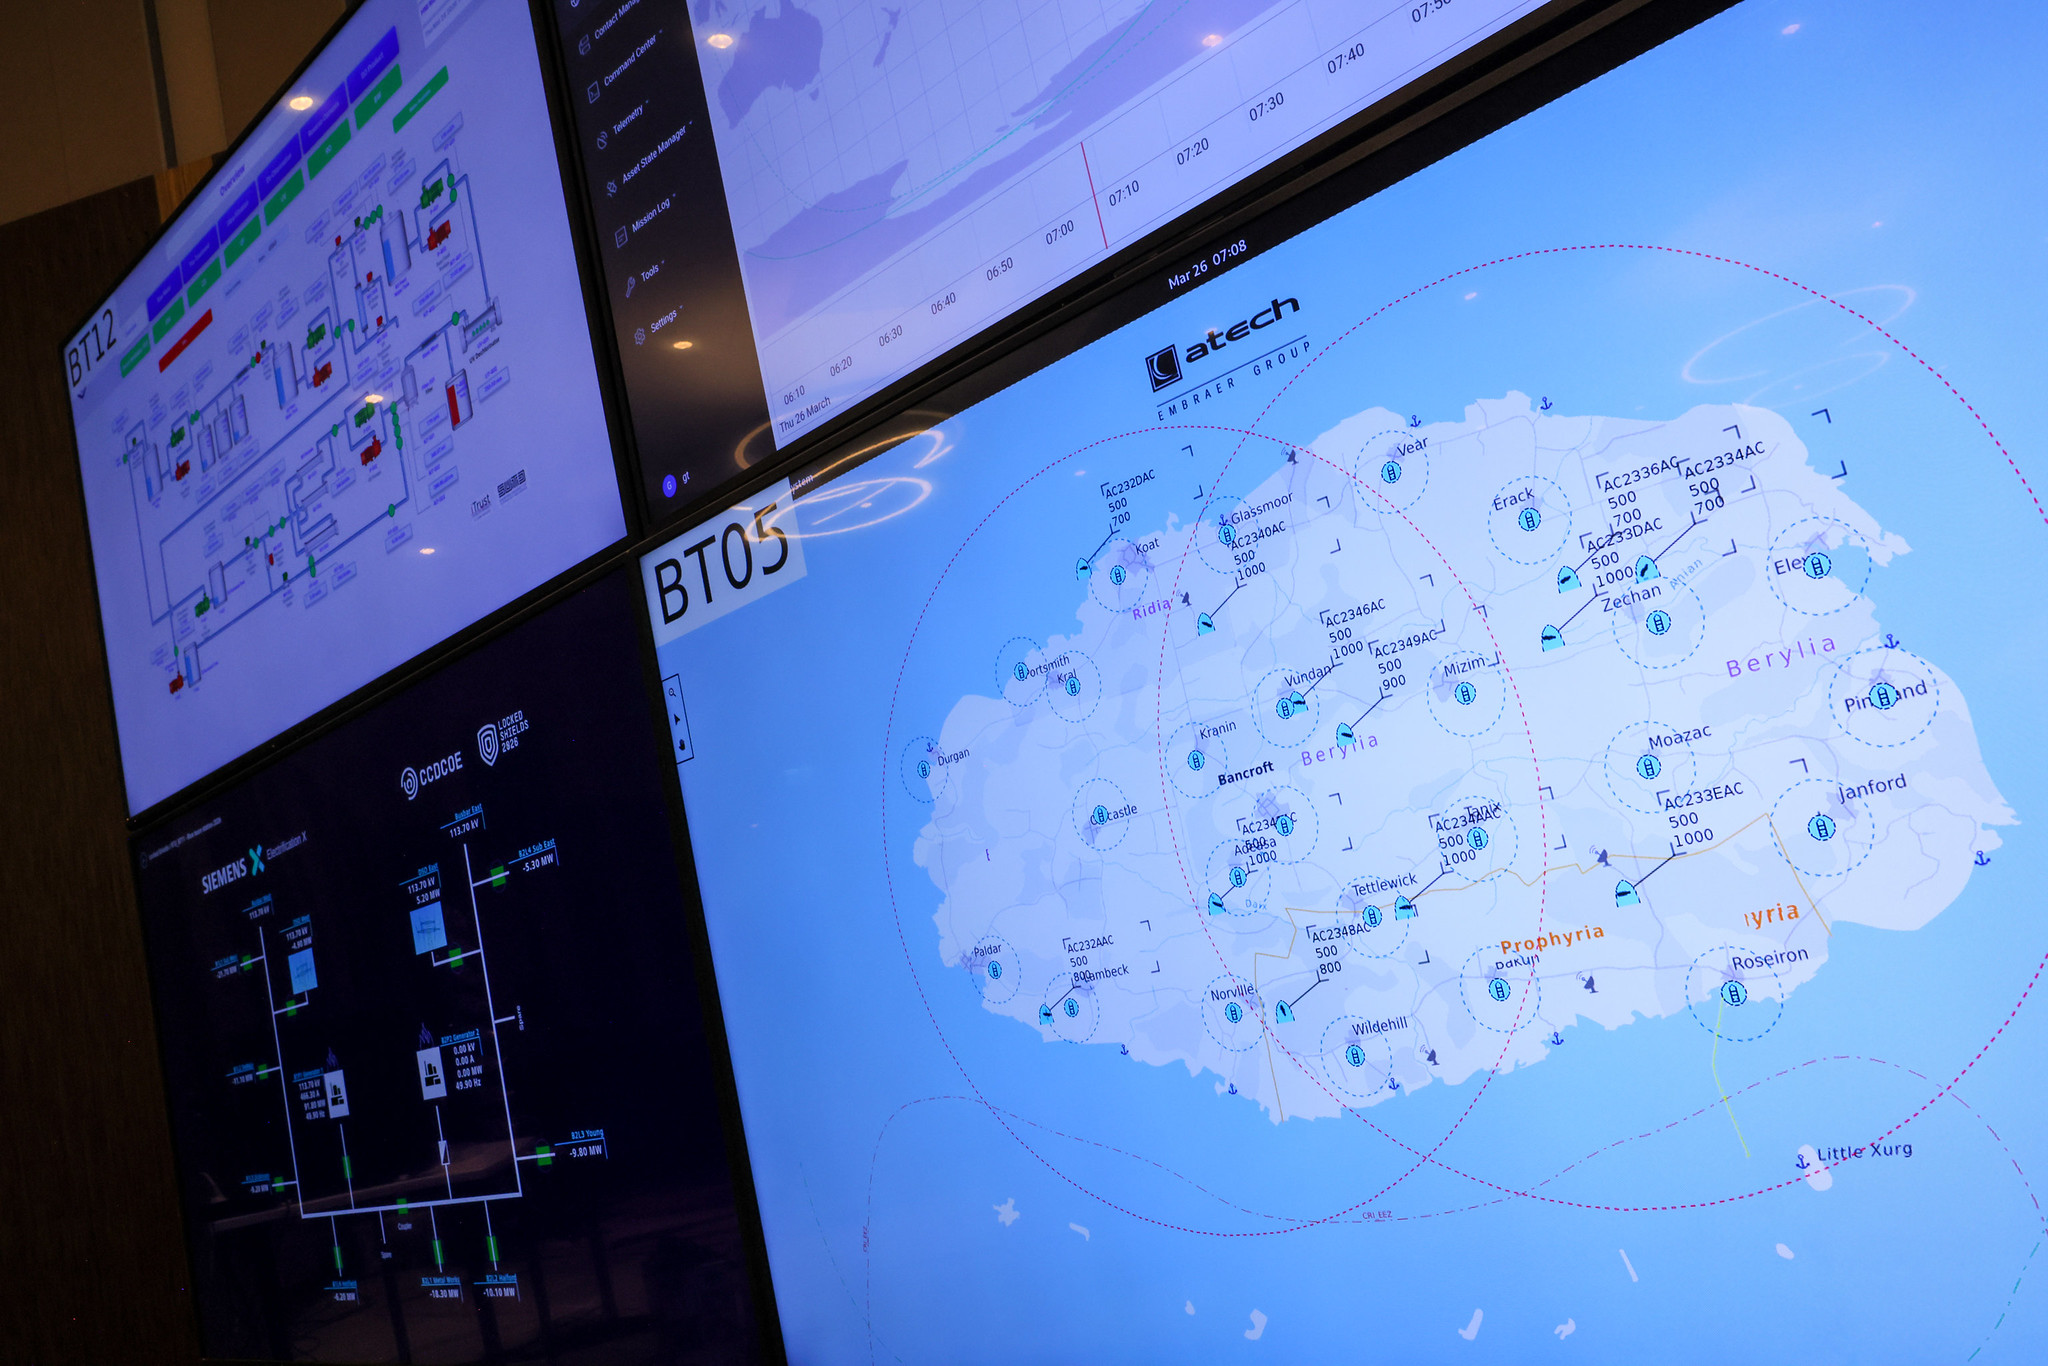
Locked Shields Partner Run 2026 – kiberbiztonság az egyetemi gyakorlatban

Az első 3 között végzett a magyar csapat a Locked Shields 2026 Partner Runon! (Pontosabb eredményt nem hírdettek a szervezők.)

A Locked Shields minden évben a világ legnagyobb és egyik legösszetettebb valós idejű kibervédelmi gyakorlataként teszi próbára a NATO szövetségesek és partnerek kiberbiztonsági szakértőit. Ennek az gyakorlatnak a “főpróbája” a Locked Shields Partner Run, amelyre a hazai egyetemek több mint tíz éve delegálnak oktatókat és hallgatókat. Nagyon jó példája ez az egyetemi kooperációnak, amelynek oktatás-kutatási és innovációs eredményeit ma már az oktatásban is használjuk. A Partner Run egyben lehetőséget terem a hallgatóknak arra, hogy az elméleti tudásukat valós körülmények között próbára tegyék. A gyakorlatot a NATO Kooperatív Kibervédelmi Kiválósági Központ (CCDCOE) szervezi Tallinnból, Észtországból.

A gyakorlat alapvetően egy “Red Team vs. Blue Team” struktúrára épül: a vörös csapat szerepe a támadás szimulálása, míg a kék csapatok – nemzeti vagy nemzetközi formációk – célja a védelmi stratégiák és technikai megoldások összehangolt alkalmazása a támadások kivédésére, és a támadó beazonosítására. A gyakorlat során a résztvevők nem csupán műszaki kihívásokkal néznek szembe, hanem a stratégiai döntéshozatal, jogi kérdések, igazságügyi feladatok és a krízis kommunikáció területén is komplex, dinamikusan változó helyzeteket kell kezelniük.

A gyakorlaton való közös részvétel már egyfajta tavaszi hagyomány a Budapesti Műszaki és Gazdaságtudományi Egyetem, az Óbudai Egyetem és a Nemzeti Közszolgálati Egyetem hallgatói és oktatói számára. Ehhez tavaly csatlakoztak az Eötvös Loránd Tudományegyetem, majd idén a Pécsi Tudományegyetem, illetve a győri Széchényi István Egyetem hallgatói is.

A szervezők által közzétett hír elérhető itt.

Posted on — Leave a comment

CrySyS dataset of CAN traffic logs containing fabrication and masquerade attacks

Our paper introducing a new CAN dataset is now available in Nature: Scientific Data.
The dataset contains 26 recordings of benign network traffic, amounting to more than 2.5 hours of traffic. We performed two attacks (injection and modification) with different configurations multiple times on each benign trace to create a comprehensive set of traffic logs. The dataset structure was explicitly designed with machine learning applications in mind.

Continue reading CrySyS dataset of CAN traffic logs containing fabrication and masquerade attacks

Posted on — Leave a comment

Gépi Tanulás & Adatbiztonsági Védekezések

Ez a blogposzt a második egy két részes sorozatból mely a gépi tanulás adatbiztonsági kockázatairól kíván közérthető nyelven egy átfogó képet nyújtani. Ez a bejegyzés a létező védekezéseket tárgyalja, míg az előző a lehetséges támadásokat mutatta be.

Continue reading Gépi Tanulás & Adatbiztonsági Védekezések

Posted on — Leave a comment

Gépi Tanulás & Adatbiztonsági Támadások

Ez a blogposzt az első egy két részes sorozatból mely a gépi tanulás adatbiztonsági kockázatairól kíván közérthető nyelven egy átfogó képet nyújtani. Ez a bejegyzés néhány létező támadást fed le, míg a következő a lehetséges védekezéseket mutatja be.

Continue reading Gépi Tanulás & Adatbiztonsági Támadások